What Crypto Wallets Do
Crypto wallets are programs or physical devices used to manage blockchain assets. They store or otherwise use cryptographic keys that authorize transactions, provide access to wallet balances, and allow a wallet to be restored or imported on another device.
A private key functions as both an authorization credential and an encrypted password for a blockchain account. Anyone who possesses the required private key can control the associated assets. This is the basis of the saying "not your keys, not your coins." If someone else gets your private key, they can move your funds without your permission.
A wallet does not necessarily hold coins as physical currency. Its role is to manage the keys and transaction-signing process associated with blockchain addresses. When you send crypto, the wallet signs the transaction with your private key and broadcasts it to the network. The wallet itself is not the coins - it is the tool that controls access to them on the blockchain.
If you have ever wondered why you need a crypto wallet , this is the core answer: it gives you a way to interact with blockchain assets without exposing your credentials to every app you use. A wallet keeps your keys organized and gives you a consistent interface to check balances, send funds, and connect to decentralized applications.
Hot Software Wallets
Software wallets, also called hot wallets, are programs that run on computers, phones, tablets, or browsers. They require an internet connection to interact with a blockchain and are commonly used for day-to-day cryptocurrency management. Because they connect to exchanges and blockchains, they can make it convenient to store, send, buy, and trade cryptocurrency. Many also support purchases with bank cards or other payment methods.
Examples of software wallets include MetaMask, Rabby, Rainbow, 1inch Wallet, and Trust Wallet. These wallets take several forms. Mobile and desktop apps are downloaded and installed directly on a phone, tablet, or computer. Some store private keys on the device and add protections such as encryption and biometric authentication. Web wallets run on a developer's servers and are accessed through a browser without a local installation. Browser extensions are installed in a browser and provide an interface similar to a web wallet. Some desktop wallets can run a full node by downloading a copy of an entire blockchain, but full-node wallets require substantial disk space and power.
Hot wallet pros and cons
- Fast internet-connected trading
- Easy setup and use
- Familiar interfaces similar to banking apps
- Direct interaction with decentralized applications
- Support for buying and selling cryptocurrency
- Support for hardware and hierarchical deterministic wallets in some implementations
- Free or low-cost download options
- Greater exposure to malware, phishing, browser vulnerabilities, compromised operating systems, and malicious applications
- Constant internet availability, which increases the number of possible attack paths
- Dependence on the security of the device, browser extension, application, and connected services
A wallet application may also be custodial or self-custodial. Software versus hardware and hot versus cold are separate classifications. A hot software wallet can be either custodial or self-custodial. Custodial wallets are managed by a legal entity or service provider that controls the private keys and, consequently, the funds. Centralized cryptocurrency exchanges such as Binance, Coinbase, and Gemini commonly offer custodial exchange accounts and web wallets.
Cold Wallets and Hardware-Wallet Terminology
Cold wallets generate and store keys outside an active internet connection. Because they are separated from online systems, they are less exposed to malware, phishing, and other online attacks. Offline signing can also reduce the risk of unintentionally approving malicious smart-contract interactions. Cold wallets for cryptocurrency are the go-to choice when you want to keep your keys away from internet-connected devices for extended periods.
The terms "hardware wallet" and "cold wallet" are sometimes used interchangeably. One classification describes a hardware wallet as a type of cold wallet. Another cautions that the terms are not exact synonyms: an unused account generated on a hardware wallet may remain cold, while an account that connects to a blockchain application is no longer strictly cold under that definition. The same material warns that approving transactions or smart-contract permissions can compromise an account's security even when the private key remains inside the device.
This terminology does not change the central function of a hardware wallet. Its private keys remain isolated from the connected computer or phone, and transaction authorization is performed inside the device. The key point is simple: the private key never leaves the hardware wallet during normal signing, even though the companion software on your phone or computer handles the transaction details.
What a Hardware Wallet Is
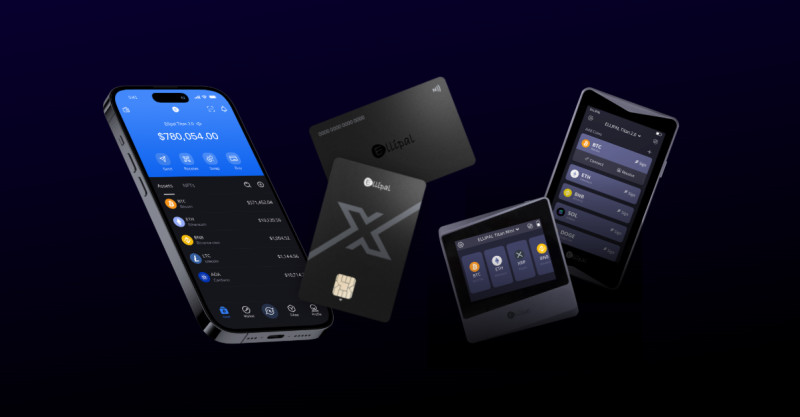
A crypto hardware wallet is a specialized physical device designed to store private cryptographic keys offline and use them to sign blockchain transactions. A device may include a secure computer chip, specialized firmware or an operating system, a small display, buttons or another physical control, USB or Bluetooth connectivity, and a PIN, passphrase, or other authentication mechanism. A hardware wallet resembles a USB drive, card, or another small handheld device.
It does not technically contain cryptocurrency coins. It contains or derives the keys needed to control assets recorded on a blockchain. A hardware wallet for crypto keeps the private key isolated from the host computer or phone. Hardware wallets such as those from Ledger and Trezor can support multiple blockchains and asset types. Some devices support many networks, while others are configured for a narrower asset set, such as Bitcoin-only firmware.
Users generally interact with a companion application on a phone or computer. The application prepares transactions, exchanges data with the wallet, and broadcasts signed transactions to the blockchain. The private key remains inside the hardware device. Hardware wallets are physical products and are not free. Their additional security comes from a combination of key isolation, local transaction processing, device authentication, firmware, physical controls, and a separate user confirmation step.
What is inside a hardware wallet
- Secure computer chip that stores and isolates private keys
- Specialized firmware or operating system
- Small display for transaction review
- Buttons or physical controls for confirmation
- USB or Bluetooth connectivity
- PIN, passphrase, or other authentication mechanism
How a Hardware Wallet Processes a Transaction
A typical transaction process follows these steps. Connect the hardware wallet to a phone or computer through USB or Bluetooth. Open the relevant wallet, exchange, decentralized application, or other interface. Select the assets, recipient, amount, fees, and other transaction conditions. The companion application constructs an unsigned transaction and sends the transaction data to the hardware wallet. The hardware wallet parses the transaction and displays its intent, meaning the full details of the unsigned transaction. The user reviews the transaction and selects an option such as sign or reject. The companion application sends the proposed transaction to the device for authorization. The hardware wallet independently asks the user to confirm the transaction through its own screen and physical controls. The device uses the private key inside its protected chip or firmware environment to create a cryptographic signature. The signed transaction is returned to the phone or computer. The phone or computer broadcasts the signed transaction to the blockchain without ever receiving the private key.
Physical confirmation on the device serves as a second authorization step and is described as two-factor authentication. The purpose is to prevent a compromised computer or remote attacker from unilaterally transacting with the private key.
The defining security property is that the private key does not leave the hardware wallet during normal signing. The connected device may see transaction details, the public address, the signed transaction, and other non-secret data, but it does not need the private key. The device's own display is also relevant to security because the device can show the recipient, amount, fees, and other transaction details without relying entirely on a browser or phone interface. A malicious or misleading host interface can still create risks if the user does not verify what is shown on the hardware device itself.
Keys, Seed Phrases, and Recovery
Hardware wallets can generate private keys for multiple accounts and blockchains. A secret recovery phrase, also called a seed phrase or master key, can restore the keys managed by the device. The recovery phrase has broad authority. Anyone who obtains it may be able to reconstruct the associated wallet and its assets. Hardware-wallet security therefore depends on both the device and the safeguarding of its recovery information.
A hardware wallet can provide offline transaction signing, PIN or passphrase protection, multiple blockchain accounts under one recovery system, recovery from a compatible backup device, separate accounts for different assets or purposes, and support for passphrases that derive additional wallets. The seed phrase is a list of random words that can be used to recover access to funds. Losing it can prevent access, while another person obtaining it can expose the funds.
Self-custody also transfers recovery responsibility to the user. If a user loses the password, private key, and recovery phrase, there is generally no third party that can restore access. The supplied wallet classification states that a paper wallet cannot be used to perform transactions by itself. Unlike a hardware wallet, it has no device interface, secure chip, display, or transaction-signing process. Paper wallets keep keys away from internet-connected devices, but their security depends on the physical paper being secured.
Benefits of Hardware Wallets
Hardware wallets are generally non-custodial or self-custodial. The user controls the private keys and therefore has direct authority over the assets. The private keys remain on a dedicated device instead of being stored in a browser extension or ordinary phone application. A compromised host does not automatically receive the key.
Transactions can be constructed online while authorization occurs inside the device. This separation allows the wallet to interact with current blockchains without exposing the private key to the connected computer. The device displays transaction information and requires physical action before signing. This provides an additional check against unauthorized transactions. A single device can manage keys for numerous blockchain addresses and assets. Some wallets support several blockchains, while others use asset-specific firmware.
Secure elements and related controls can protect key operations against physical extraction, tampering, and side-channel analysis. The level of protection depends on the device architecture and implementation. Offline signing and physical review can reduce the chance of blindly approving malicious contract permissions. This protection depends on correctly understanding transaction details and verifying the information displayed by the device. Hardware wallets are well suited to holding assets for longer periods because the device can remain disconnected and securely stored between transactions. For long-term holding, this is one of the best crypto storage options available today.
Limitations of Hardware Wallets
Hardware wallets are physical products with a purchase price. A second device, multisig setup, recovery equipment, or replacement plan adds further cost. Initial setup can be challenging for beginners. Users must understand seed phrases, device authentication, companion software, supported assets, firmware updates, and transaction verification. Not every wallet supports every coin, token, blockchain, or smart contract. Devices may also have version-specific compatibility requirements.
A hardware wallet generally needs to be connected to another device for each transaction. It is less convenient for frequent trading or routine payments than a software wallet. The device must be stored securely and remain available when transactions or recovery are needed. A lost, damaged, stolen, or malfunctioning device can interrupt access unless a backup arrangement exists. More wallets also mean more PINs, passphrases, backups, locations, inventories, and devices that must remain synchronized with the intended wallet design.
The phone or computer interface is still part of the transaction process. While it does not receive the private key, malware, browser compromise, or deceptive interfaces can affect what transaction data is presented to the user. A hardware wallet can protect a key while still signing a transaction that the user does not understand. Users must inspect recipients, amounts, fees, token contracts, permissions, and network details on the trusted device display. Incorrect setup of multisig arrangements can cause permanent loss of access, so the configuration, backup shares, signer list, threshold, and software must be tested and documented.
Hot Wallets Compared with Hardware Wallets
Hot wallets are designed for frequent access and internet-connected use. They are convenient for trading, decentralized applications, exchanges, and daily management. Their private keys are more exposed to the device, browser, operating system, and software supply chain. Hardware wallets are designed to keep key operations separate from the internet-connected environment. They are less convenient for frequent use but provide stronger isolation for long-term holdings.
A hardware-wallet setup can also be used with a hot companion application. The application prepares and broadcasts transactions, while the hardware wallet retains the keys. This combines software convenience with device-based signing without making the private key part of the software wallet. The hot and cold wallet cryptocurrency debate comes down to this: hot wallets for access, hardware wallets for isolation. Which one fits depends on how often you trade, how much you hold, and how much risk you are comfortable with day to day.
Choosing a Hardware Wallet
Relevant security features include device PIN or passphrase protection, independent physical transaction confirmation, transaction and recipient display, multisignature support, secure element or equivalent protected key storage, firmware authentication and signed updates, backup or recovery-seed support, protection against side-channel and physical attacks, and open-source or independently auditable components. One selection framework specifically asks whether the device offers two-factor confirmation, multisignature capability, and a recovery seed backup.
Some devices are designed for beginners, while others provide more advanced controls. The interface should make it possible to verify transaction details without excessive complexity. Important interface questions include whether the device has its own screen, whether a user can inspect the recipient, amount, fees, and permissions, whether controls are understandable, whether the companion software supports the intended networks, whether transactions can be rejected safely, how passphrases are entered, and how firmware updates are installed and verified.
Full hardware wallet comparison checklist
- Key isolation and secure-element use
- Open-source firmware and reproducible builds
- Independent audits and clear update process
- Device screen and transaction-detail display
- PIN and passphrase behavior
- Recovery options and multisig support
- Supported coins and networks
- USB and Bluetooth compatibility
- Exchange and decentralized-application support
- Companion software quality
- Manufacturer reputation and firmware responsiveness
- Physical size and durability
- Price
- Backup plan
- Post-quantum readiness
Open-source software can make behavior easier to inspect. If software is not open source, it should be securely developed and independently audited. Reproducible builds allow security experts to compare the code a manufacturer says is running with the code running on the device. Open-source code, reproducible builds, audit reports, and a clear update process all help establish what is operating inside a wallet. Reproducibility also makes it easier for researchers to locate areas where a wallet could potentially expose private-key material.
A buyer should confirm support for every coin, token, blockchain, account type, and contract they intend to use. Hardware wallets may differ in their support for Bitcoin, Ethereum, Solana, XRP, other chains, tokens, staking, and smart contracts. Some users choose a dedicated Bitcoin-only wallet for simplicity or security. Other devices support a broad range of assets. The manufacturer's reputation, operating history, customer feedback, support quality, firmware responsiveness, and security track record are relevant comparison points. Reviews can provide insight into setup, compatibility, recovery, and everyday use.
A recovery phrase is an essential part of self-custody. Buyers should understand how the phrase is generated, displayed, backed up, and protected. Additional recovery options may include a second hardware wallet restored with the same wallet, steel or other durable physical backup media, Shamir secret sharing, multisignature shares, and a backup device stored separately. A hardware wallet can still be compromised before it reaches the buyer. Supply-chain attacks can tamper with devices during manufacturing, distribution, or delivery, so checking for signs of tampering and securing the device from the factory through setup is essential. When you are ready to move funds off an exchange , a hardware wallet is often the best cryptocurrency cold wallet option for self-custody.
Whether One Hardware Wallet Is Enough
For Trezor devices, one unit is described as enough to protect assets under ordinary conditions. A second hardware wallet can add security, flexibility, and operational continuity, but it also creates another device and recovery arrangement that must be managed. A single device may be sufficient when its supported assets match the user's needs, the recovery phrase is securely backed up, the user can replace it after loss, damage, theft, or failure, the device architecture supports the required long-term algorithms, and the user does not need a multisig or separated operational setup.
A second device becomes more relevant when immediate access is needed after the primary device fails, long-term and trading funds need different operational policies, business and personal assets must be separated, travel requires a limited-balance wallet, inheritance or multisig access is planned, devices are needed for teaching or demonstrations, different firmware or asset-support requirements cannot be combined, or the user wants redundancy across separate physical devices.
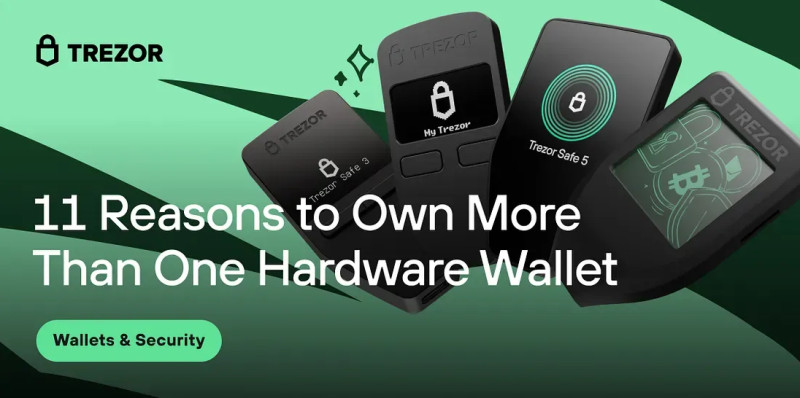
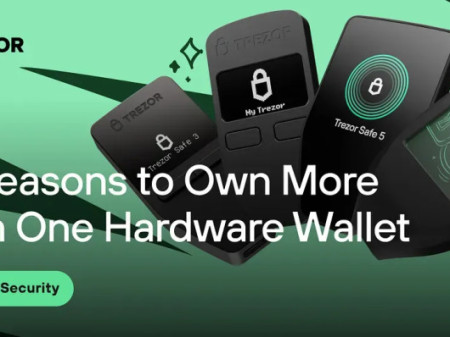
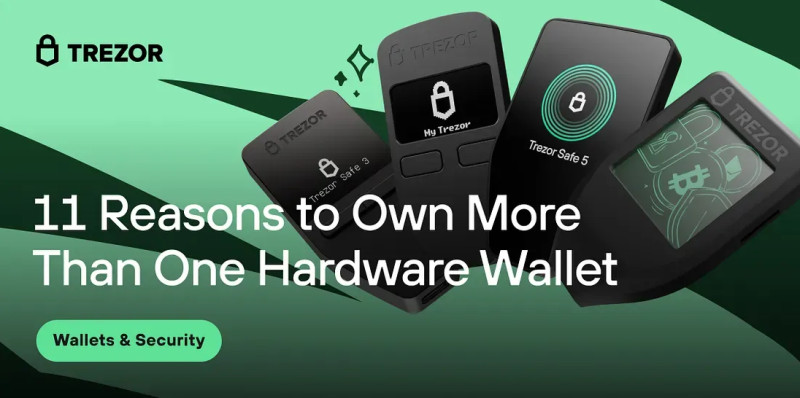
Reasons to Own More Than One Hardware Wallet
There are several practical reasons to own a second hardware wallet. A backup device can provide continuity if the primary device is damaged, lost, stolen, misplaced, destroyed, or no longer available for purchase. The primary wallet can be kept in regular use while a second device is stored securely. If the primary device fails, the backup can be restored with the same wallet credentials rather than requiring the user to wait for a replacement. The article describes this as cloning or restoring the original wallet onto another hardware device. The two devices will usually be kept in different locations.
A hardware wallet can introduce another person to self-custody without requiring the recipient to leave assets on an exchange. The giver can also help with setup, recovery, and transaction verification. Some users want a Bitcoin-only device and a separate device for other assets. Trezor Safe 3 and Trezor Safe 5 are described as having Bitcoin-only firmware options. Bitcoin-only firmware may simplify the interface and reduce the number of supported applications or attack surfaces for users who hold only Bitcoin. Separation can also apply to long-term Bitcoin holdings and other experimental or actively used assets.
An actively traded wallet is connected and used frequently. A long-term wallet is touched less often and can be stored securely. A two-device arrangement can provide a frequently used trading wallet and a rarely touched long-term wallet, with reduced handling of the long-term device and a clear separation between active and passive holdings. A user who holds Bitcoin and altcoins may keep one device for long-term storage and another for active transactions. Multiple wallets can divide funds across devices, reducing the effect of a single theft, loss, or hardware failure.
11 reasons to own more than one hardware wallet
- Emergency backup and continuity if the primary device fails
- Gifting to introduce someone to self-custody
- Separate Bitcoin from other cryptocurrencies with different firmware
- Separate trading from long-term storage
- Asset and device diversification to reduce single-point risk
- Inheritance planning for family or executor access
- Business funds separation for company assets
- Travel with a limited-balance wallet
- Collecting and upgrading to newer hardware
- Teaching and demonstrations without risking personal holdings
- Multisignature security arrangements for groups or organizations
A hardware-wallet owner may need to consider whether family members or an executor can locate and use the wallet after an emergency or death. Questions include whether the family knows where the device is stored, whether they know how to unlock it, whether they can recover the wallet, whether multiple devices or signers are required, whether the inheritance arrangement is documented, and whether a multisig setup would prevent one person from unilaterally taking all funds. Giving a hardware device to a trusted family member or executor is one approach discussed. It may be combined with multisignature authorization or Trezor's Multi-share Backup.
Shared Recovery Phrases and Cloned Backup Devices
Two independently created crypto wallets can theoretically share the same recovery phrase, but the odds are described as practically impossible. A different arrangement is where two devices are cloned by restoring the same original wallet to both devices. In that case, both devices intentionally contain the same wallet and recovery information. A user who is new to hardware wallets is advised to begin with one primary wallet and one backup device. Additional devices can then be added when asset separation, business operations, travel, inheritance, teaching, or multisignature requirements justify the added management.
Security Principles for a Wallet System
No cryptographic system is truly unhackable. Wallet security must be treated as an ongoing process because the operating environment, software dependencies, user interfaces, connected services, and physical devices can all become attack surfaces. A crypto wallet is a system rather than a single key-storage product. Robust protection requires cryptography, specialized software, hardware boundaries, secure user interfaces, transport protection, recovery design, and risk modeling.
Wallet attack surfaces can include memory-unsafe runtimes, mobile operating-system vulnerabilities, malicious or compromised open-source dependencies, third-party cryptographic libraries, JSON parsers, browser permissions, application programming interfaces, user-interface components, companion applications, network connections, physical access to a device, firmware-update processes, and recovery flows. Even audited, open-source systems can fail through an interaction between otherwise valid components. A secure design therefore examines how weaknesses in one layer can be chained with another layer to produce a larger exploit.
Trusted execution environments, such as Apple's Secure Enclave or Android's StrongBox, can isolate cryptographic operations from the rest of an operating system. A dedicated secure element can generate, store, and use private keys while preventing the main processor from reading raw key material. Multi-party computation allows multiple parties to cooperate on a signature without reconstructing the complete private key. Threshold signatures use a quorum of participants or key shares, so authorization can remain available if one participant is compromised, while no single participant can sign alone. Key lifecycle management covers generation, use, rotation, backup, recovery, retirement, and compromise response throughout the wallet's lifecycle.
Code defenses include formal verification of critical paths, static analysis to identify memory leaks and unsafe permissions, continuous integration with security checks, and dependency isolation and auditing for third-party libraries. Reproducible builds allow observers to verify that the released source code corresponds to the binary running on the device. Open-source firmware exposes signing logic and trust assumptions to independent review, but it does not remove the need for testing, audits, secure manufacturing, and physical design.
User Interface and Transport Security
A user interface is a security boundary, not merely a presentation layer. A cryptographic wallet can fail if the interface misrepresents what the user is authorizing. Potential visual protections include wallet fingerprints, color-based interface cues, domain-binding indicators, consistent transaction-display formats, and clear warnings when a site or application cannot be verified. Seed generation must use high-quality randomness, and interfaces should warn against weak entropy sources and user-selected seed phrases that can be guessed or copied.
Safer defaults include avoiding persistent seed-phrase display, disallowing clipboard access where possible, expiring inactive sessions, limiting application permissions, requiring local confirmation for sensitive actions, and avoiding unnecessary exposure of account information. Every exchange between a wallet, companion software, exchange, decentralized application, or service can be an interception point. Transport protections include TLS with certificate pinning, nonce-based challenge-response protocols, mutual authentication using ephemeral keys or secure tokens, session integrity checks, and authentication at both the user and service ends. The wallet should verify that the service is authentic, and the service should verify that the wallet or user is authentic.
Recovery Design and Social Recovery
Most wallet compromises are described as resulting from user error during recovery rather than from the normal signing operation. Recovery is therefore part of the primary security boundary. Shamir's secret sharing can divide a secret into an n-of-m arrangement, with a defined threshold required for reconstruction. Shares can be stored in separate trusted environments. Social recovery can make access easier for a user, but it introduces risks involving collusion, impersonation, and social engineering. The recovery process requires cryptographic safeguards and careful verification. Hardware-bound derivation combines the seed phrase with biometric or device-specific entropy, making wallet reconstruction dependent on a particular device or context. Recovery design must balance usability with security. A wallet is not secure if normal transaction signing is protected but its recovery process can be manipulated or taken over.
Post-Quantum Readiness in Wallet Design
Quantum computing may not have a predictable arrival date, but the potential impact on long-lived signatures is significant. Wallets designed today need a migration path if blockchains replace elliptic-curve algorithms. Post-quantum protections include key-rotation infrastructure, hybrid signatures that combine classical and post-quantum schemes, signature-algorithm abstraction layers, firmware-update paths that can install new algorithms, memory and flash capacity for larger signatures, and physical protection against side-channel leakage. Post-quantum readiness is based on modularity and migration planning rather than deploying a single unconfirmed standard before networks decide which schemes they will require.
The National Institute of Standards and Technology finalized its first post-quantum digital-signature standards in August 2024: ML-DSA, FIPS 204, a lattice-based standard formerly associated with Dilithium, and SLH-DSA, FIPS 205, a hash-based standard formerly associated with SPHINCS+. Existing hardware wallets were built primarily for elliptic-curve signatures rather than post-quantum cryptography. Whether a current device can add post-quantum signing depends on where signing takes place, whether the secure element exposes new algorithms, how firmware is verified, available flash and RAM, transaction and UI resource requirements, side-channel resistance, whether the bootloader can be updated, and whether the current trust boundary permits the new algorithm.
Architecture Differences Matter
Ledger uses a dual-chip architecture: a secure element runs Ledger OS and performs cryptographic operations, while a separate microcontroller manages USB, Bluetooth, and the display. Ledger describes the separate microcontroller as a "dumb router" that does not perform application logic or store secrets. Signing occurs inside the secure element through operating-system calls. Key derivation also occurs in the secure element. Secure elements identified in recent Ledger devices include ST33J2M0 in Nano X and ST33K1M5C in Nano S Plus, Stax, and Flex. Published STMicroelectronics specifications list the ST33J2M0 with 50 KB user RAM and up to 2,048 KB user flash, and the ST33K1M5C with 64 KB user RAM and up to 1.5 MB user flash. Ledger OS and its isolation mechanisms consume part of that capacity, leaving less available for any new signing feature.
Running post-quantum signing on the separate microcontroller would conflict with Ledger's stated trust boundary because that microcontroller is not permitted to handle key material. Post-quantum support therefore requires secure-element platform support. Trezor uses a different trust model: recent devices may include a secure element that enforces physical access controls, but transaction signatures are computed in firmware on the main microcontroller. The firmware is open source, which allows the signing path to be independently audited and allows algorithm upgrades without requiring direct secure-element vendor involvement or new secure-element certification.
Memory remains a limitation for Trezor. It uses a streaming protocol for Bitcoin signing because an entire transaction may not fit in device memory. Some Bitcoin transactions can be several hundred kilobytes, while older Trezor devices have 64 KB of total memory. Newer Safe devices use STM32U5-series microcontrollers with up to 2 MB flash and 786 KB RAM, or higher-end variants with up to 4 MB flash and 2.5 MB RAM. Post-quantum code would still compete with transaction parsing, user-interface rendering, safety checks, firmware update logic, and existing signature algorithms. The Trezor architecture makes firmware-based ML-DSA support more plausible, but the main microcontroller does not provide the same built-in physical countermeasures as a secure element.
Post-Quantum Signature Size, Speed, and Memory
Traditional signature sizes include ECDSA at 64 to 72 bytes and Ed25519 at 64 bytes. Post-quantum signatures are substantially larger: ML-DSA-44 produces a 2,420-byte signature and 1,312-byte public key, while the smallest SLH-DSA parameter set yields a 7,856-byte signature. A device that already needs streaming to process transactions within limited memory may face additional difficulty when signatures are approximately 30 to 120 times larger than conventional signatures. Larger signatures can affect transaction size, memory requirements, broadcast time, blockchain data storage, fee calculation, confirmation behavior, and device parsing and verification.
The pqm4 project has benchmarked post-quantum cryptography on Cortex-M4-class microcontrollers. Reported SPHINCS+ signing times on a 24 MHz Cortex-M4-class system range from 22 seconds to 88 minutes. ML-DSA is faster, but its rejection-sampling process introduces variable timing. Timing variation affects both user experience and side-channel analysis because observable execution time may depend on secret-dependent values. Trezor's STM32U5 processor runs at 160 MHz, which provides more performance than the cited 24 MHz benchmark platform. Signing must still complete within a user-acceptable approval window alongside transaction parsing and display work.
RAM is often the main implementation constraint. Standard pqm4 implementations of Dilithium, now ML-DSA, reportedly require approximately 50 to 100 KiB on Cortex-M4-class systems. Memory-optimized implementations have reduced usage, with compact Dilithium3 demonstrated below 12 KiB and further work reducing key generation and signing below 7 KiB. On a Ledger secure element with 50 to 64 KB of total user RAM shared with Ledger OS, the standard 50 to 100 KiB requirement may exceed the available space for one signing operation. On a Trezor microcontroller with up to 786 KB RAM, ML-DSA fits more comfortably, but it still shares memory with transaction parsing, interfaces, and safety checks.
Side-Channel Resistance and Upgrade Feasibility
A hardware wallet assumes that an attacker may have physical access. The attacker may measure power consumption, timing, electromagnetic emissions, voltage changes, and other physical side channels. Classical ECDSA and EdDSA implementations on embedded devices have years of accumulated hardening, including constant-time code, blinding, and other countermeasures. Post-quantum schemes have less implementation history. Specific concerns include ML-DSA rejection sampling creating observable timing variation related to secret data, Falcon having implementation risks involving its sampling process and floating-point arithmetic, and timing, power, and electromagnetic leakage revealing information about intermediate values or keys.
A secure-element-centric design inherits more physical countermeasures from the chip, but only if the secure element supports the new algorithm. A microcontroller-centric design offers more firmware flexibility, but the implementation team carries more responsibility for physical and side-channel hardening. For many currently deployed devices, at least one of the three conditions for post-quantum support is absent: the signing architecture can add the algorithm without crossing or weakening the device's trust boundary, the device has enough CPU, RAM, flash, and battery or timing capacity to run it, and the device has a secure firmware path for receiving and authenticating the implementation.
Some newer microcontroller-based devices with post-quantum boot chains, including Trezor Safe 7, are positioned to add ML-DSA-class transaction signing through firmware updates. For many legacy devices, both secure-element-based and older microcontroller-based products, post-quantum transaction signing may require hardware replacement. The dependency between wallet vendors and blockchain developers is circular: wallet vendors must choose which algorithms to support before blockchains finalize their requirements, blockchain developers must consider whether deployed wallets can run the selected schemes, hardware takes years to design and manufacture, secure elements take years to develop and certify, and chain migrations require consensus and coordination.
Users holding significant value in a classical-only hardware wallet are advised not to assume the current device will carry them through the transition. This does not mean the device must be replaced immediately, but a future replacement should be evaluated for its firmware-verification architecture, algorithm support, resource headroom, and migration path.
The different type of crypto wallets you choose today should be evaluated partly for post-quantum readiness, because hardware takes years to design and manufacture, and chain migrations require consensus and coordination. Recommended ecosystem actions include shipping post-quantum boot chains in every new hardware wallet, designing new devices with enough RAM and flash for ML-DSA alongside classical algorithms, supporting hybrid signatures during transition periods, having secure-element vendors expose ML-DSA and SLH-DSA through common cryptographic interfaces, requiring chain developers to evaluate the capabilities of deployed wallets before selecting mandatory algorithms, evaluating the next hardware purchase partly for post-quantum readiness, and avoiding the assumption that every current hardware wallet will receive a complete post-quantum upgrade.
Hardware-Wallet Design Principles for Future Security
Future wallet security will depend on the interaction between physical devices, software, networks, user interfaces, and recovery systems. Keys should remain within trusted hardware or distributed cryptographic processes. Secure elements, trusted execution environments, multi-party computation, and threshold signatures can reduce single points of compromise. Wallet software should separate algorithm implementations from transaction formats and user interfaces, allowing a signature scheme to change without redesigning the entire wallet. Wallets need infrastructure for rekeying and algorithm migration, as rotation may be required by a quantum threat, a discovered cryptographic weakness, or routine key-lifecycle management.
A hybrid transaction can carry both classical and post-quantum signatures during migration, with verification requiring both to prevent a failure in one system from silently removing the other. Recovery needs the same attention as transaction signing. Shamir shares, multisig, device-bound derivation, and carefully verified social recovery can reduce dependence on a single seed or device. A wallet should reveal only the information and controls needed for the current task. Seed phrases should not remain permanently displayed, and clipboard or application access should be limited. Open-source code, reproducible builds, static analysis, formal verification, dependency audits, and signed firmware updates make it easier to identify whether the implementation matches its stated design.
Signing code must be designed to resist power, timing, electromagnetic, and other side-channel attacks, especially for algorithms that have not yet received years of embedded-device hardening. A hardware wallet is a signing appliance. The host constructs an unsigned transaction and sends it over USB or Bluetooth. The device displays transaction details such as the recipient, amount, and fees. The user approves with a physical action. The device returns a signature while the private key remains inside the hardware. The location of signing and the components allowed to touch key material determine whether new post-quantum algorithms can be added later.
Comments on “Crypto Hardware Wallets: How They Work and What You Should Compare”
No comments yet. Be the first to share your thoughts.