What Crypto Companies Should Know About Web3, Risk, and Payments
Crypto companies are not just coin projects. In the source material, they include exchanges, payment firms, wallet makers, marketplaces, banks, fintechs, treasury tools, and infrastructure providers. These businesses touch cryptography, public blockchains, customer money, public policy, and old bank systems at the same time.
I don’t see this as one clean market. The useful question is not whether crypto is “decentralized.” It is easier to ask four plain questions: Where does trust sit? What law touches the product? Can the payment system move money at a fair cost? What can break when an outside service fails?
Trust Never Disappears
Cryptographer Matthew Green draws a line between removing trust and extending trust. A promise such as “I promise not to look” can become a technical limit such as “I cannot,” but that limit still rests on trusted software, hardware, keys, networks, and service operators.
“I promise not to look” can become a technical “I cannot.”
Trust often returns at the edges. A blockchain may hold ownership data while a wallet, API provider, marketplace, identity service, or payment partner controls what the user sees and does. A protected contract can still sit inside a system that leaks data through metadata or outside tools.
Trust anchors named in the source
- Software code and release processes
- Hardware that holds or protects keys
- The method used to generate keys
- The network that stores and sends data
- The company or public body that runs the service
That changes the questions a crypto company should ask. It is not enough to say that a key stays in a wallet. The company also needs to know which service supplies balances, which market shows an NFT, which partner handles a payment, and who can change each part.
Why Web3 Often Runs Through Central Platforms
People do not want to run their own servers. That fact has pushed much of the Internet toward companies that host websites, mail, storage, and trading tools for users. Protocols also change more slowly than platforms because a broad protocol needs agreement, while one company can ship a new feature fast.
Marlinspike points to email staying unencrypted for decades while WhatsApp moved from unencrypted messages to end-to-end encryption in about a year. He also contrasts hard-to-change standards on IRC with platforms such as Slack, which can add items like custom reaction emojis with little friction.
His two decentralized apps were normal React websites. Their state and permission rules sat on a blockchain, but phones and browsers still spoke to hosted Ethereum nodes. Infura and Alchemy became key access points, and MetaMask often relied on Infura when an app needed blockchain data.
Some API replies were unsigned JSON. A client could ask for the result of a contract view and trust the provider’s answer without checking blockchain state itself. The same setup can expose reads, link wallet accounts, and show which apps and users are connected.
Where a Web3 app can lean on a central service
- Hosted node access through providers such as Infura and Alchemy
- Unsigned blockchain data returned through an API
- Wallet connections that can link separate accounts
- NFT display data supplied by a marketplace such as OpenSea
- Transaction history supplied by an Etherscan-style service
“Accept that users will not run their own servers.”
NFTs Show the Trust Problem
Most image NFTs do not keep the image itself on-chain. The token often points to a URL on a normal web server, and many NFT standards did not require a hash that locks the token to the exact file a buyer saw. An owner, server operator, or future domain holder could change what the link returns.
Marlinspike built an NFT that served different media by requester. It looked like one thing on OpenSea, another on Rarible, and an excrement emoji through a crypto wallet. The token stayed the same while its visible meaning changed with the request path.
Even a non-custodial wallet did not have to run the whole system. MetaMask could keep keys on the client while using outside data for balances, history, and NFT display. In Marlinspike’s test, an OpenSea “304 No Content” reply was enough to make a token vanish from the wallet even though its ownership record remained on-chain.
Protocols Can Stall While Platforms Move
Marlinspike’s First Derivative app exposed a protocol limit. The app wanted to price an NFT derivative as a share of the underlying NFT, but its value came from an OpenSea API. ERC-721 did not support royalties, and changing the standard after deployment was too late, so marketplaces added their own royalty settings.
That gave platforms control over parts the protocol did not define. OpenSea, Coinbase, Etherscan, Infura, and Alchemy could shape prices, data, features, transaction rules, and the way users saw ownership. In Marlinspike’s experimental marketplace, accepting one NFT bid could also cost about $80 to $150 in Ethereum fees.
Platforms that can shape a protocol in practice
- OpenSea can supply market prices and control NFT display
- Coinbase can shape how assets are bought, sold, and held
- Etherscan-style services can supply transaction records
- Infura and Alchemy can supply blockchain access and add data tools
- Wallets can filter or hide assets based on outside API replies
Marlinspike called the market an “engine or a leaky bucket.” Spending that stayed inside crypto could feed the cycle, while moving proceeds into old assets could weaken it. His point was not that every Web3 product must copy a platform. It was that familiar platform habits tend to return unless the product accounts for them.
Stablecoins Move Crypto Toward Payments
If you’ve searched what coins are stablecoins , the plain answer in this source is simple: stablecoins are crypto assets used to move and settle value while connecting with money that firms already use. The focus is payment rails, treasury, and settlement rather than speculation alone.
A business can use stablecoins for cross-border payments, treasury moves, payroll, payouts, and settlement between firms. The goal is not to remove banks or accounting. It is to add another path for moving funds, often between crypto and fiat and crypto currency through on-ramps and off-ramps.
Networks covered in the stablecoin report
- Ethereum
- TRON
- Polygon
- Solana
- Base
- Binance Smart Chain
- Avalanche
- Stellar
- The Lightning Network
The source does not cover how to invest in stablecoins . It treats stablecoins as business tools. A firm still has to test redemption, wallet access, fees, timing, custody, accounting, and the legal rights attached to each asset before placing real funds at risk.
Enterprise Payments and Treasury Use
Merge presents stablecoins as a way for firms to settle on crypto rails instead of relying only on correspondent banking. Its service model includes stablecoin payments, multi-currency accounts, an API, fiat on-ramps and off-ramps, embedded payment tools, and payment reconciliation.
A multi-currency account can hold, send, and receive funds in more than 60 currencies through one account. A business can also receive local payment details such as EUR IBANs, while payment orchestration coordinates several providers, routes, currencies, and payment conditions rather than acting as one simple gateway.
Business uses listed for stablecoin rails
- Sending international business payments
- Holding and moving treasury liquidity across countries
- Running payroll in employees’ preferred currencies
- Making global payouts
- Automating payment initiation, routing, and settlement
- Repatriating revenue
- Bridging stablecoins and fiat
- Collecting brokerage deposits and disbursing local currency or stablecoins
For a US business, USD crypto settlement can sit beside dollar payments rather than replace them. The source points to faster access to liquidity, clearer payment records, and lower cross-border costs, but those gains still depend on the chosen network and service path.
If you are looking for the most crypto-friendly banks , the source does not rank them. A better test is whether a bank can connect with stablecoin rails, handle local currency accounts, reconcile records, and explain who controls keys and customer funds at each step.
Recurring Stablecoin Subscriptions
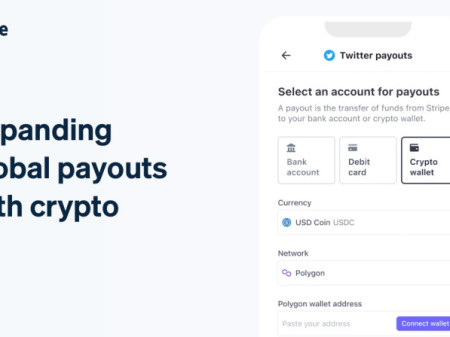
Stripe’s subscription design targets firms whose recurring payments can be costly, slow, or hard to accept across borders. Stripe reported that 30% of its business customers had recurring models. It also cited one company that moved about 20% of payment volume to stablecoins and said the cost per transaction was half as much.
A normal blockchain payment asks the wallet owner to sign each transfer. Stripe’s contract lets a customer save a wallet as a payment method and authorize recurring payments without signing every charge. The launch described in the source supported more than 400 wallets, USDC on Base and Polygon, and direct fiat settlement.
“Stablecoin payments help us reduce our cost of revenue for payments from all around the globe, attract more tech-forward users, and reach folks who don’t have access to other payment methods.”
For crypto companies, this turns online crypto currency payments into a managed subscription flow. The customer sees a familiar payment method, while the company gains a blockchain-based charge and fiat payout. The hard parts move into wallet support, contract permissions, refunds, and account rules.
Tokenized Securities Still Carry Securities Rules
A tokenized security is an instrument that meets the legal definition of a security and is represented as a crypto asset, with ownership records held at least partly on a blockchain. The key test is its economic substance and legal rights. Putting ownership on-chain does not remove those rights or turn the asset into something else.
The source says existing requirements still apply. Offers may need registration or an exemption, tokenized common stock remains equity, and exchanges, brokers, custodians, transfer agents, and other market participants remain subject to fraud and securities rules. Putting a record on a public network does not by itself create a safe harbor.
Questions for a tokenized security issuer
- How do holders move between tokenized and traditional formats?
- How do dividends, proxies, and other corporate actions work across both formats?
- Do the token and non-token shares still have substantially similar rights?
- How are on-chain records reconciled with beneficial-ownership reports?
- Which record is authoritative when the issuer and transfer agent disagree?
The source also describes possible self-executing lockups, easier vote counting, and smoother settlement. Those ideas could cut manual work, but they can also add legal and operating headaches. The Project Crypto framework discussed in the source remained a proposal, so companies should not treat a possible exemption or new capital route as available law.
“Individual investors, not the SEC, should make the decision.”
Tokenized Market Infrastructure
Tokenization can affect a public company even if it never issues a token. Changes to trading, custody, settlement, voting, and recordkeeping can alter how investors hold stock and how issuers handle corporate actions. The company may feel the change through its transfer agent, broker, exchange, or shareholder services rather than its own product.
Market groups named in the source
- Broadridge and its Distributed Ledger Repo platform
- The Depository Trust Company and its tokenization pilot
- Nasdaq and its proposed rule tied to the DTC pilot
- The New York Stock Exchange and its planned tokenized-securities platform
- Coordination work between the SEC and Commodity Futures Trading Commission
The case for tokenized records is plain: fewer manual steps, clearer ownership data, and faster handling of votes or settlement. The case against is just as plain. A shared ledger can create new questions about bad inputs, disputed records, outside service failures, and rules that differ across systems.
For a public company, the near-term work is mapping records and service roles. That means knowing which transfer agent holds the master record, how tokens behave during a dividend or vote, and what happens if a wallet, chain, custodian, or exchange is unavailable.
Compliance Is a Product Requirement
A TRM Labs report described two UK-registered crypto exchanges linked to Iran’s Islamic Revolutionary Guard Corps and about $1 billion in crypto movement. The available source does not give a transaction breakdown, exact volume by exchange, or the controls used by those firms. It still shows why crypto firms need records and screening that can be checked.
Controls named for crypto-market compliance
- Transaction monitoring across wallets, exchanges, and payment routes
- Customer screening before accounts or services are approved
- Beneficial-owner checks for linked accounts and entities
- Geographic controls tied to sanctions and local law
- Auditable records that explain why a transaction was allowed or blocked
- Clear rules for upgrades, account reviews, and reported suspicious activity
Compliance affects product design, licensing, and operations. A company cannot add a new wallet, token, payment partner, or trading pair without asking what rules apply, what data is needed, and who owns each check.
That includes US crypto exchanges , overseas exchanges, banks, payment companies, and any firm that holds or moves customer assets. The sanctions case is not proof of a universal playbook, but it makes one point clear: vague controls are not good enough when money may move across many services and borders.
Anonymous Credentials and Verifiable Compliance
Some rules ask a service to confirm that a user meets an age, location, license, or regulatory test. A common response is to collect a government ID. Anonymous credentials aim to prove only the needed fact without showing the same identity to every website or linking all uses back to one document.
David Chaum’s model separates credential issuance from credential use. The issuer checks identity and signs a credential, but the website sees a valid credential rather than the issuer’s record of the person. A wristband is a useful analogy: a bar checks that the wristband is valid, not the driver’s license used to get it.
Facts a selective crypto credential could prove
- The holder lives in the United States
- The holder does not live in New York
- The holder is at least 25 years old
- The underlying identity document has a valid government signature
Zero-knowledge proofs can prove those claims without showing the hidden fields. That matters for a crypto exchange, wallet, or token service that needs age or location rules but does not need a user’s full address, birth date, or document number.
Copies are the hard part. The source describes single-use credentials, revocable credentials, and credentials tied to phone hardware. Privacy Pass puts the single-use model into practice through blind signatures, while richer claims can use zero-knowledge systems that prove selected facts without exposing a stable user identifier.
Security Lessons From Keys and Proofs
Green’s review of XChat shows how provider trust can weaken an encrypted system. XChat lacked Signal-style forward secrecy, and private keys were held through X’s key system under a password or PIN. Splitting key work across several servers can reduce one server’s power, but it does not remove the need to trust the people who run them.
A six-digit PIN has about one million possible values. Slow key derivation helps, but it cannot stop unlimited online guesses. Stronger setups cap attempts, protect the counter inside hardware, or split the secret so an attacker must reach a set number of independent servers.
Kerberoasting attacks older Windows networks that use human-set service-account passwords. A user can request a Kerberos ticket, take it offline, and try many passwords with fast hardware. The source cites a jump from about 6.8 million AES guesses per second to about 4.18 billion guesses per second when a service falls back to RC4 and weak NT hashing.
Fiat-Shamir proof systems offer a different warning. They turn a verifier’s random challenge into a hash. A proof can fail if the circuit being proved can compute the same hash and shape its output around a weak challenge, so the program description and full transcript must be tied into the check.
Security checks supported by the source
- Keep private keys away from services that should not control them
- Cap online password guesses and protect the attempt counter
- Retire legacy password and encryption settings
- Bind the full circuit, program, and transcript into a Fiat-Shamir challenge
These are not side notes. Each case shows the same pattern: a strong inner tool can still fail through key storage, weak passwords, legacy settings, or a bad link between a program and its proof.
Where Trust, Law, and Payments Meet
Here is the map I use for crypto companies: follow the money, data, keys, rights, and outside services from start to finish. A product can use a public blockchain and still depend on a private API, a wallet maker, a payment bank, a market maker, a custody provider, and a legal regime.
Questions tied to the source
- Which software, hardware, keys, networks, and operators must users trust?
- Which app data comes from an outside API, and is that data checked against the chain?
- Which company holds keys, transaction history, balances, and NFT media?
- Where do stablecoin payments enter and leave through fiat on-ramps and off-ramps?
- What network fees, bid costs, custody fees, or payment costs can block a small transaction?
- Which legal rule applies to a token, wallet, exchange, payment, or tokenized security?
- Which record is authoritative when a blockchain and an outside transfer agent disagree?
- What identity facts must be collected, and can a proof reveal only what the service needs?
- How are customers, owners, wallets, and partners screened for sanctions and fraud risk?
- What happens when an API, chain, wallet, payment partner, key, or legal rule is unavailable?
Comments on “What Crypto Companies Should Know About Web3, Risk, and Payments”
No comments yet. Be the first to share your thoughts.